Data security and AI
Connecting your data to AI has become easy. Doing it securely still takes expertise.
Before entrusting your restaurants’ data to an AI assistant, put in place the access controls, permissions and maintenance needed for professional use.
An assistant that compares sales across your restaurants, explains a drop in margin or prepares a weekly summary: AI applications are becoming tangible for restaurant groups.
It is now possible to build an initial demonstration quickly. A few connections, accessible data, and the tool starts answering questions.
But before entrusting it with information from your entire group, one question deserves as much attention as the quality of its answers: what have you actually given it access to?
When the prototype becomes an everyday tool
It all starts with a test at one restaurant. The results go down well, so the other sites are added. One manager asks for access. Then another. A few weeks later, the tool is being used to prepare for management meetings.
Meanwhile, the account used for testing has retained its broad permissions. A personal key has been left in a configuration file. No one has clearly taken over responsibility for updates.
The problem arises when the tool is used professionally, but access controls and maintenance remain those of a prototype.
Experimenting with fictitious data and limited permissions allows you to move quickly. The transition to real data must become an explicit step, with a review of the architecture, access controls and responsibilities.
Reading the figures does not require the ability to change them
An assistant tasked with comparing sales generally does not need to make changes in the till system. To analyse staff costs, it does not need to change staff rotas.
Yet the account used to connect these software systems may have all these permissions.
OWASP uses the term ‘excessive agency’ for the risk associated with functions, permissions or autonomy that are too broad for the task assigned to the AI. Writing ‘never modify the data’ in an instruction is not equivalent to technically removing permission to modify it. Restrictions must be enforced in the connected systems.
Read-only access still needs to be controlled. A manager may need sales figures for their own restaurant without being able to view those of the entire group or the individual details of every employee.
A document can contain more than information
An assistant can read invoices, emails or web pages. This content can also contain instructions intended to redirect its behaviour: asking it to find confidential data and then send it on, for example.
This is the principle behind indirect prompt injection. The content being consulted attempts to become an instruction for the assistant.
An instruction to ignore these attempts is not enough. It is also necessary to limit accessible data, control the available tools and govern transmissions to external destinations. For a sensitive action, human approval provides an additional check, provided that what will be sent or changed is clearly presented.
Preparing a data layer suited to AI
For a restaurant group, one approach is to bring useful information together in a structured data warehouse: sales, purchases, stock, staff costs and restaurant master data.
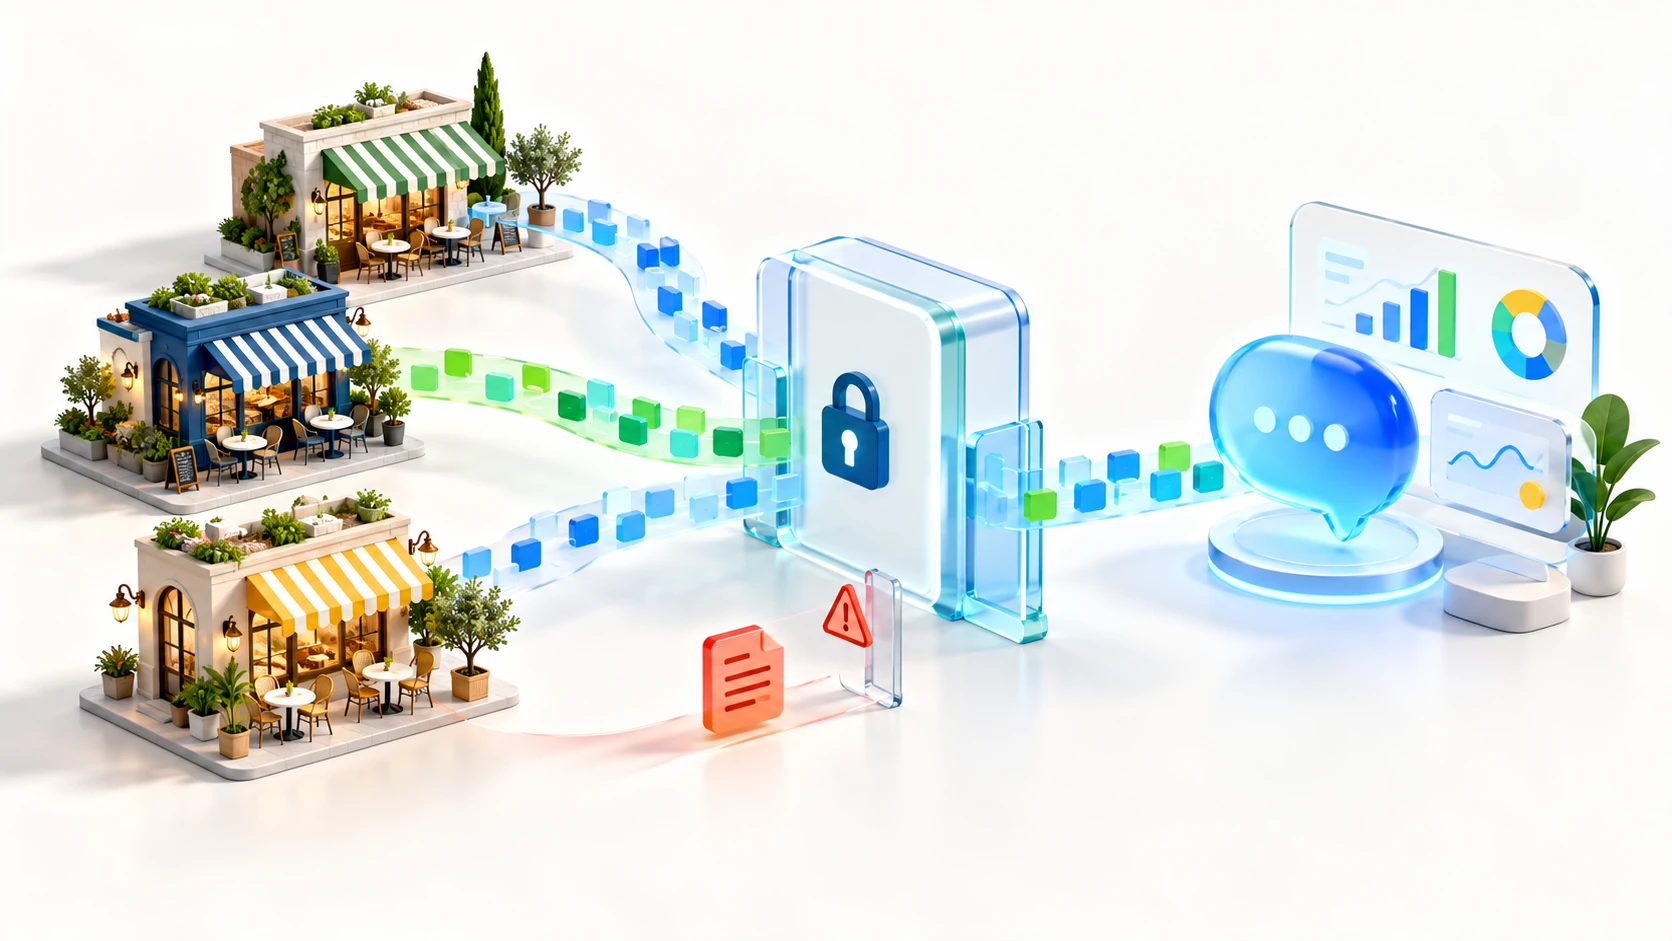
This layer makes it possible to bring sources together, standardise metrics and prepare the data needed for analysis. The assistant can then access it through targeted tools: viewing sales for a given period, comparing restaurants it is authorised to access or retrieving a margin metric.
Each tool exposes a specific function and checks the user’s permissions. This makes it possible, for example, to allow a regional director to view their area, while senior management has a consolidated view.
This architecture also allows analytical requests to be handled without giving the assistant access to functions that make changes in the till system or staff rotas.
However, a data warehouse concentrates sensitive information. It too must be protected, maintained and monitored. Its value depends on how access is designed and controlled.
Five questions before going into production
The security of an AI project also rests on the fundamentals of any professional application:
- Who can access what? Dedicated accounts, permissions limited to what is needed and multi-factor authentication for sensitive human access.
- How are secrets protected? Keys and passwords kept out of code and logs, with a procedure for revocation and renewal.
- How are environments maintained? Testing kept separate from production, up-to-date software and services exposed only when necessary.
- Can usage be traced? Access and actions logged without unnecessarily accumulating sensitive data.
- Who steps in if there is a problem? A designated person in charge, access that can be cut off and backups whose restoration has been tested.
These answers must be concrete before the tool becomes essential to the group’s operations.
Moving from a demonstration to a lasting tool
A prototype helps identify the uses worth developing. Turning it into a lasting tool then requires preparing the data, defining permissions and organising maintenance.
At TucoData, we help restaurant groups bring their data together and structure it for reporting, analysis and AI. This work starts with your sources and business needs, but also with an essential question: what information should each user and each tool be able to view?
Are you preparing a data or AI project for your restaurant group? Let’s discuss your data sources and integration needs.
Further reading